Mobile Security & APK Inspector

APK & Mobile Sports App Safety Checker: Sideloading Risk Inspection

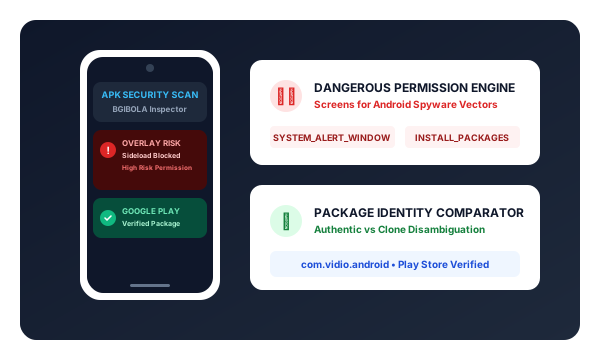
Inspect Android sports streaming applications and APK package identifiers to compare distribution sources, identify deceptive brand clones, and evaluate high-risk mobile permissions.

✓ Google Play Authenticity Check
✓ Tapjacking Overlay Detection
✓ Permission Risk Profiler
APK Safety Checker
Mobile Application Legitimacy Audit

APK & Streaming App Checker

Check whether a mobile sports streaming application originates from verified official app stores, inspect package identifiers, and review dangerous Android permission hazards.

Quick Sample Applications:

Critical Android Permissions to Never Grant to a Sports Streaming App

High Risk

SYSTEM_ALERT_WINDOW

Draw Over Other Apps (Overlay)

Can generate deceptive invisible screens over banking or login apps to steal credentials (tapjacking).

Critical Risk

BIND_DEVICE_ADMIN

Device Administrator Access

Grants control over system security policies and prevents users from uninstalling the application normally.

Critical Risk

REQUEST_INSTALL_PACKAGES

Install Unknown Packages

Allows the app to download and silently install secondary malicious payloads in the background.

Critical Risk

BIND_ACCESSIBILITY_SERVICE

Accessibility Services

Enables full screen reading, simulated touch events, and keystroke logging across all other applications.

High Risk

READ_SMS

Read SMS Messages

Can intercept two-factor authentication (2FA) verification codes sent via SMS.

Medium Risk

READ_CONTACTS

Access Contacts & Phonebook

Exfiltrates user address books for phishing campaigns or spam distribution.

How to Audit an Android Sports Streaming Application

1

Locate Package Identifier

Find the Android package name (formatted like com.brand.app) in the app settings, or paste the download link into the inspection form.

2

Verify Distribution Source

The auditor cross-references the download origin against the official Google Play Store registry to confirm developer identity.

3

Audit Requested Permissions

Compare the app permissions against our dangerous permission database to check for tapjacking, SMS snooping, and package installations.

4

Follow Safety Recommendations

Avoid sideloading untrusted binaries and install verified broadcaster apps exclusively from authorized app stores.

The Severe Security Hazards of Sideloading Sports APKs

Many unofficial sports portals instruct mobile visitors to “Download our Android APK” to bypass web browser ads or access purported free streaming servers. Sideloading—the practice of downloading and executing an .apk file outside the Google Play Store—disables vital automated defenses including Google Play Protect.

High-Risk Exploits Common in Pirated Sports APKs:

  • Screen Overlay Attacks (Tapjacking): Applications requesting SYSTEM_ALERT_WINDOW can render an invisible transparent layer over banking or crypto apps, intercepting PIN entries and authorization touches.
  • SMS & 2FA Code Interception: Applications requesting RECEIVE_SMS can read incoming one-time passwords (OTPs) sent by financial institutions, allowing unauthorized account takeovers.
  • Silent Background Downloader: Using REQUEST_INSTALL_PACKAGES, a seemingly benign sports app can download secondary malicious payloads after initial installation without user awareness.
  • Device Administrator Hijacking: Malicious APKs prompt users to grant Device Admin rights, preventing uninstallation and locking the device with ransomware demands.

Android Dangerous Permissions Reference Matrix

Android Permission Severity Level Threat Vector & Abuse Pattern
SYSTEM_ALERT_WINDOW Critical Risk Tapjacking, UI overlay manipulation, login harvesting over banking screens.
RECEIVE_SMS / READ_SMS Critical Risk Interception of two-factor authentication (2FA) verification codes.
REQUEST_INSTALL_PACKAGES High Risk Silent sideloading of secondary Trojans and cryptominers without approval.
BIND_ACCESSIBILITY_SERVICE Critical Risk Keystroke logging, automated screen reading, unauthorized screen clicks.
READ_EXTERNAL_STORAGE Moderate Risk Exfiltration of private photos, documents, and cached application files.

Frequently Asked Questions

What is an Android Package Identifier (Package ID)?
An Android Package Identifier is a unique namespace (e.g. com.vidio.android) assigned by developers to identify their application in the Android operating system. Pirated copies frequently use modified or generic package IDs to impersonate official apps.
Is it ever safe to download a sports streaming APK from a forum or telegram group?
No. Installing applications distributed through forums, file lockers, or messaging groups carries extreme risk. Attackers frequently modify original APK binaries to embed spyware payloads while retaining the working video player interface as a disguise.