Technical Methodology, Evaluation Criteria & Data Sources
In-depth technical documentation detailing the algorithms, data models, heuristic scanners, and primary sources powering BGIBOLA sports utilities.
✓ UTC ISO-8601 Standardization
✓ RFC-Compliant Protocols
1. Match Scheduling & Timezone Architecture
Live sports fixtures span across dozens of global time zones. To eliminate conversion discrepancies between daylight-saving transitions and regional standards, BGIBOLA operates a centralized temporal architecture:
- Temporal Ingestion Standard: Every fixture kickoff timestamp is parsed and stored exclusively in synchronized UTC ISO-8601 notation (e.g.,
2026-10-17T19:00:00Z). - Dynamic Client-Side Calculation: Match countdowns and kickoff clocks calculate time deltas client-side against the browser’s native JavaScript
Intl.DateTimeFormatAPI and standard IANA timezone databases. - Cross-Hemisphere Precision: When Daylight Saving Time changes occur asynchronously between the UK/Europe and North America, our system dynamically adjusts hour offsets to prevent inaccurate kickoff listings.
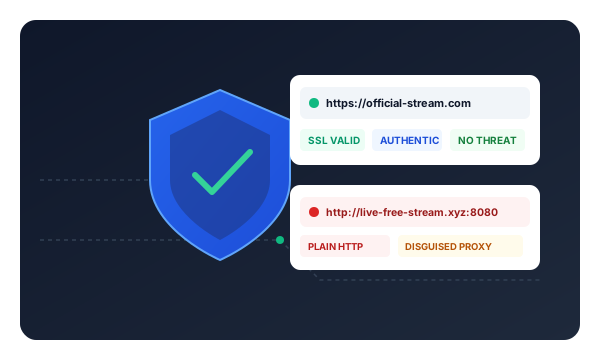
2. Link Safety Checker: Algorithmic Threat Heuristics
Our Link Safety Checker evaluates user-submitted streaming URLs through a five-stage heuristic evaluation pipeline designed to detect common deceptive patterns:
Transport Layer Security (TLS/SSL)
Checks for valid HTTPS protocol enforcement. Unencrypted HTTP endpoints are flagged with an immediate security penalty due to man-in-the-middle risks.
Punycode & Homoglyph Spoofing
Inspects hostnames for RFC 3492 Punycode prefixes (xn--) often used to disguise Cyrillic or Greek lookalike characters mimicking reputable brands.
Domain Age & Dynamic DNS Heuristics
Flags hosts utilizing dynamic DNS providers (e.g., DuckDNS, No-IP) or ephemeral domain generation algorithms frequently associated with disposable pirate mirrors.
Suspicious TLD Risk Weighting
Applies calibrated threat weighting against high-risk top-level domains commonly exploited for malware distribution and aggressive malvertising redirection.
Redirect Expansion & IP Scoring
Audits URL shortener chains and raw IPv4/IPv6 host addresses, alerting users to multi-hop redirection patterns designed to obscure end destinations.
3. APK Safety Checker: Android Permission Taxonomy
The BGIBOLA APK & App Checker analyzes Android application package metadata and manifest declarations to evaluate whether a sports streaming app poses device security hazards:
| Android Manifest Permission | Security Classification | Risk Vector in Streaming Apps | Threat Weight |
|---|---|---|---|
SYSTEM_ALERT_WINDOW |
High Risk / Special Access | Enables draw-over overlays, facilitating tapjacking attacks that intercept keystrokes or banking screen inputs. | Critical |
RECEIVE_SMS / READ_SMS |
Dangerous Permission | Allows rogue applications to intercept one-time two-factor authentication (2FA) passcodes sent by banks. | Critical |
BIND_ACCESSIBILITY_SERVICE |
Critical System Privilege | Grants automated screen reading and programmatic tapping capabilities, often abused by sophisticated banking trojans. | High |
REQUEST_INSTALL_PACKAGES |
High Risk | Permits the application to silently download and prompt installation of secondary malware payloads. | High |
READ_EXTERNAL_STORAGE |
Dangerous Permission | Enables broad inspection of device photos, documents, and private local media files. | Moderate |
4. Stream Calculator: Mathematical Bandwidth Models
Our Streaming Rights & Bandwidth Calculator calculates data consumption using industry-standard bitstream throughput formulas across primary video codecs:
Data (GB) = [ Video Bitrate (Mbps) + Audio Bitrate (Mbps) ] × Duration (Seconds) × 1.20 (Transport Overhead) ÷ 8,192
Our model incorporates a 20% buffer overhead factor to account for TCP retransmissions, HLS/DASH manifest polling, and container transport framing, delivering real-world accuracy rather than theoretical minimums.
Explore Our Interactive Utilities
Test these algorithms yourself using our live tools: Link Safety Checker, APK Checker, and Streaming Calculator.