BGIBOLA Link Safety Checker: Inspect Sports Streaming Links
Analyze unfamiliar sports streaming links and suspicious domain names for phishing indicators, deceptive punycode, unencrypted protocols, and disguised redirection tricks before you click.
✓ 100% Client-Side Privacy
✓ Zero Data Logging
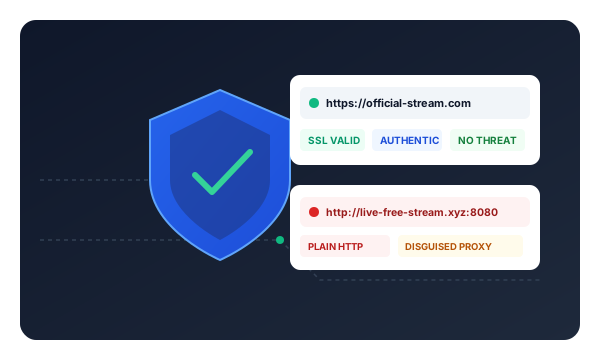
BGIBOLA Link Safety Checker
Analyze unfamiliar sports streaming links and suspicious domain names for phishing indicators, deceptive punycode, unencrypted protocols, and disguised redirection tricks.
Transport Encryption
Verifies whether the link enforces HTTPS. Plain HTTP addresses allow network snooping, credential injection, and script tampering.
Homoglyph & Punycode Check
Detects internationalized domains (xn--) designed to look identical to legitimate brands like Sky, beIN, or Vidio using Cyrillic or Greek alphabets.
Deceptive Subdomains & Ports
Flags chained subdomains and anomalous network ports commonly configured on disposable proxy servers and phishing redirectors.
How the Heuristic Safety Engine Inspects Web Addresses
Input Suspicious Domain or URL
Paste the web address or click one of our curated sample addresses to inspect common threat indicators.
Real-Time Structural Analysis
The scanner parses DNS hostnames, transport encryption protocols (HTTPS vs HTTP), port configurations, and Punycode encoding.
Detailed Security Breakdown
Review eight automated security checks with color-coded risk flags (Pass, Caution, Warning) and technical findings.
Actionable Defense Guidance
Follow tailored defensive steps to protect your browser, personal credentials, and banking security from threat actors.
The Reality of Risks on Unofficial Streaming Websites
Sports fans searching for free live match feeds frequently believe the only inconvenience is video buffering. In reality, cybersecurity research demonstrates that illicit sports streaming portals are major distribution channels for malware, scareware, and credential harvesting.
Common Threat Vectors on Illicit Streaming Portals:
- Transparent Clickjackers & Invisible Overlays: Layered elements placed over the video player that trigger background browser tabs to open affiliate scams or malicious APK downloads when you attempt to click play or unmute.
- Fake Video Codec Prompts: Modal popups claiming your browser requires an urgent “HD Video Extension” or “Media Codec Update”, which install data-stealing extensions that inject adware into your search results.
- Homoglyph Brand Impersonation: Attackers register domain names substituting ASCII characters with visually identical Cyrillic or Greek symbols (e.g., using Cyrillic “о” instead of Latin “o”) to fool users into believing they are on a legitimate sports site.
- Unencrypted HTTP Communications: Many disposable pirate portals avoid TLS certificates, exposing all user activity and submitted details to plain-text packet sniffing on public Wi-Fi networks.
Automated Security Checks Reference Matrix
| Security Check | Standard Evaluated | Security Implication |
|---|---|---|
| Transport Encryption | HTTPS (TLS 1.2 / 1.3) Enforcement | Plain HTTP allows man-in-the-middle data interception and code injection. |
| Host Representation | DNS Hostname vs Raw IP Address | Direct IP addresses frequently mask bulletproof hosting and evasive command servers. |
| Character Encoding | Punycode (xn--) Detection |
Detects internationalized domain spoofing designed to mimic official brand names. |
| Link Obfuscation | Known URL Shortener Filters | Shortening services obscure true destination domains and evade reputation filters. |
| Subdomain Structure | Excessive Chained Labels | Deep subdomain hierarchies often indicate disposable redirectors and phishing kits. |
| Network Port | Standard Web Ports (80 / 443) | Non-standard high ports (e.g. 8080, 8443) often indicate rogue proxy relay networks. |